We hack itbefore they do.
Independent security consulting, penetration testing and investigations for governments, law enforcement and enterprises. We test what you have built, find out what happened when it fails, and stay until it is fixed.
- Governments
- Law enforcement
- Financial institutions
- Critical infrastructure
Practice
What we advise on
Six areas, one team. Most engagements start in one of them and end up touching two or three.
- 01
Security architecture
Design systems that hold up under attack, from identity and network to cloud and applications.
- 02
Risk management
Know which risks matter most, what they would actually cost you, and what it takes to close them.
- 03
Compliance
Map your controls to the frameworks your regulators, insurers and customers keep asking about.
- 04
Incident readiness
Plans, playbooks and drills, so the first real incident is not the first rehearsal.
- 05
Financial crime advisory
Controls, monitoring and policy for fraud, money laundering and digital asset exposure.
- 06
Due diligence
Assess the security of a company, a supplier or an acquisition before you commit to it.
Testing
Penetration testing
Most of what we do is advice. This is the part where we get hands on, and test your systems the way a real attacker would.
- Authorised in writing before anything starts
- Scope and timing agreed with you in advance
- Run to avoid disruption to live services
- Findings ranked, with the evidence and the fix
Web applications
The sites and portals your customers and staff log in to every day.
Networks and infrastructure
Internal and external networks, servers, devices and the paths between them.
Cloud environments
Accounts, identities and configurations across your cloud estate.
People and process
Phishing and social engineering, to see how far an attacker gets past the technology.
Fraud and financial crime
Embezzlement, scams, money laundering and payment fraud, traced through accounts, companies and people.
Cyber incidents
Breaches and ransomware: how they got in, what they touched, what was taken and who is behind it.
Digital forensics
Phones, computers, accounts and logs examined and preserved so the evidence stands up to scrutiny.
Crypto and asset tracing
Funds followed across wallets, chains, bridges and mixers to the exchanges and the people at the end.
Investigations
Full investigations
When something has already gone wrong, we find out what happened, who did it and where it went, and give you evidence you can act on.
- Confidential from the first conversation
- Evidence collected and preserved so it holds up
- Findings you can take to police, regulators or lawyers
- Support through recovery and whatever comes next
Approach
How an engagement runs
No surprises and no retainer you cannot explain. Four stages, agreed up front, with a fixed scope before any work begins.
Stage 1
Scope
We agree in writing what we are looking at, what matters most to you and what the work has to deliver.
Stage 2
Assess
We review your systems, controls, documents and people, and test the assumptions underneath them.
Stage 3
Report
You get findings ranked by what they would cost you, each one with the evidence behind it.
Stage 4
Support
We help you fix what we found, then come back and check that it held.
Clients
Who we work with
Organisations that are regulated, targeted, or both. Every engagement is confidential, and we never name a client without permission.
Governments
National security, defence and public bodies.
Law enforcement
Agencies building or reviewing technical capability.
Financial institutions
Banks, payment firms and digital asset businesses.
Critical infrastructure
Energy, telecoms, transport and utilities.
Enterprises
Organisations with something worth protecting.
About
Who you would be working with
A small practice, led by the person who does the work. You deal with the people who wrote your report, not an account manager.
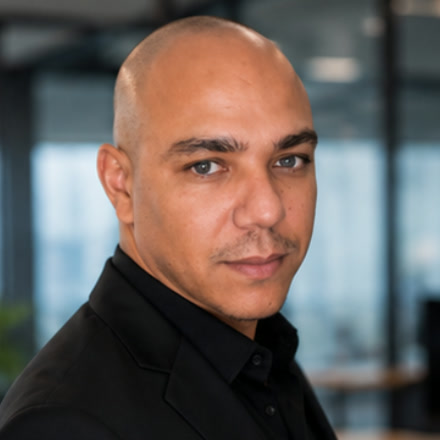
Every organisation I have tested thought it was secure. Better to hear it from us than from whoever comes next.
Work with us
Start with a confidential conversation
Tell us what you are responsible for and what is keeping you up at night. We will tell you honestly whether we are the right people for it.